CoinsAQ summary · neutral
MEV Bot Front-Runs $7.7M Ethereum Wallet Exploit
What happened
An MEV bot known as “Yoink” front-ran an attacker attempting to exploit a custom Safe module, capturing the stolen rsETH before Kelp temporarily froze the receiving address. An attacker exploited a custom module connected to an Ethereum Safe wallet in an attempt to extract.
Related asset context
Not financial advice. News and sentiment can be incomplete, delayed, or change quickly.
Continue researching
Related stories
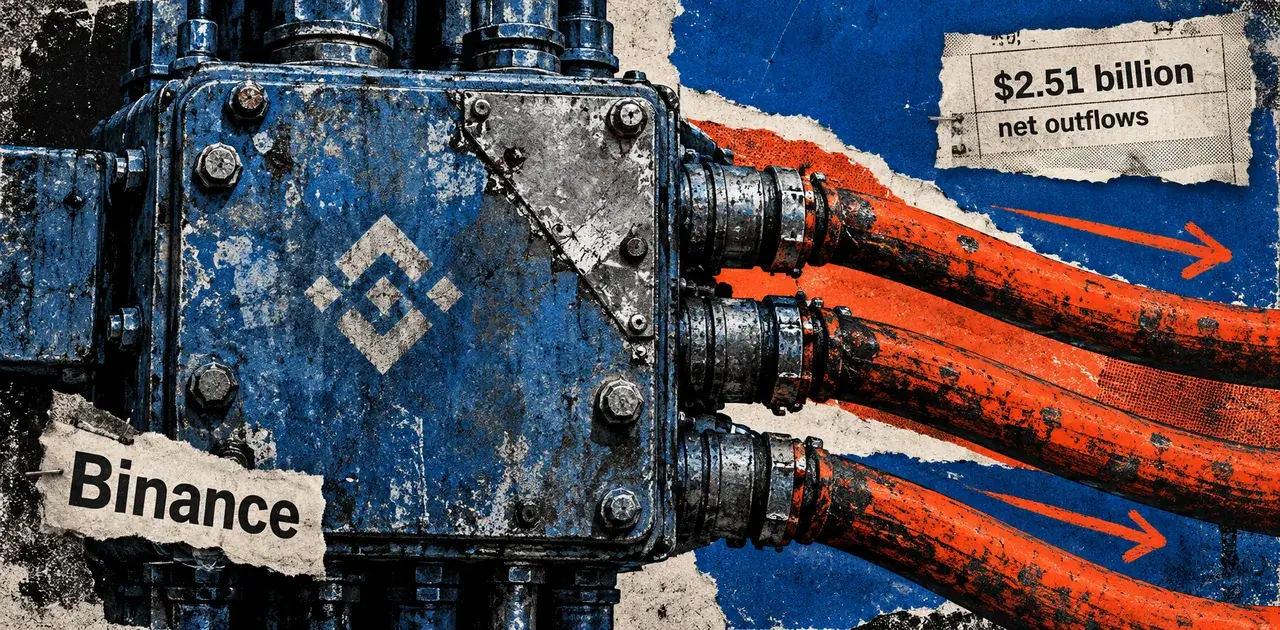
Tracked Binance wallets record $2.5 billion in outflows as withdrawals reopen after hack
Tracked Binance wallets recorded $2.5 billion in outflows as withdrawals reopened. New withdrawal wallets complicate estimates of customer exits.
Threshold Says tBTC Operators Patched or Went Offline Over Linux Flaw
Threshold detailed Linux kernel precautions and a separate operator account drain as tBTC minting and Bitcoin redemptions remain paused.
Cursor urges credential resets after malicious Claude Code marketplace update
Cursor urges cleanup and credential rotation after malicious Claude Code marketplace packages; uninstalling may leave persistence on affected hosts.